Cybersecurity for Parking Systems: What Operators Don’t Think About Until It’s Too Late
Parking operators don’t typically think of themselves as managing cybersecurity risk. They manage parking. But modern parking infrastructure — networked pay stations, cloud-connected management software, LPR cameras, payment processing systems, building access integration — represents a technology attack surface that security professionals would immediately recognize as significant.
The wake-up calls have been arriving. There have been documented cases of parking management software held for ransomware, pay station hardware compromised for payment card skimming, and access control systems breached through poorly secured parking infrastructure. The parking industry’s cybersecurity posture has generally lagged behind the technology it has deployed.
This piece maps the actual attack surface of a modern parking system, describes the real threat scenarios, and provides a practical framework for risk reduction.
The Attack Surface of a Modern Parking System
Before you can defend something, you need to understand what you’re defending. The cybersecurity attack surface of a typical modern parking operation includes:
Pay Station Hardware
Networked pay stations are computers running operating systems and software, connected to payment processing networks. The attack vectors:
Physical access to the unit interior. A technician-accessible interior contains the computing hardware, network connections, and potentially USB ports. Physical access to the interior (either through an unlocked cabinet or a compromised key system) enables installation of malicious software, capture of payment card data, and unauthorized access to the facility network via the pay station’s network connection.
Remote management interfaces. Many pay stations include remote management capabilities that allow configuration and diagnostics over the network. If these interfaces use default credentials, weak authentication, or unencrypted connections, they’re remotely exploitable.
Payment card skimming. This is the best-known attack: a device installed in or on the card reader that captures card track data. Modern NFC-only readers are more resistant to skimmers than hybrid chip/NFC readers, but determined attackers continue to develop skimming devices that defeat anti-skimming measures.
LPR Cameras and Computer Vision Infrastructure
IP cameras of any type — LPR, occupancy, security — are a well-documented vulnerability category. The attack vectors:
Default credentials. A significant percentage of installed IP cameras are still running with default usernames and passwords. Search engines like Shodan index internet-accessible cameras; default-credential cameras are searchable and accessible to anyone.
Unpatched firmware. Camera firmware vulnerabilities are regularly discovered and published. Cameras running outdated firmware with known vulnerabilities are trivially exploitable.
Network lateral movement. A compromised camera provides a foothold on the facility network. From there, an attacker can attempt lateral movement to higher-value systems: parking management servers, access control systems, or the corporate network if the parking network is inadequately segmented.
Parking Management Software
The central management software is the highest-value target in the parking system. It contains transaction history, customer data (potentially including payment card data if data minimization practices aren’t followed), operational configurations, and access credentials.
Cloud-hosted platforms face the attack vectors common to all SaaS applications: credential compromise (phishing, credential stuffing), API vulnerabilities, and third-party integration supply chain risks.
On-premise deployments additionally face the attack vectors of self-managed infrastructure: unpatched operating systems and application software, misconfigured network access, and inadequate backup/recovery practices that increase the impact of ransomware.
Integrations and APIs
Every integration between parking systems is a potential attack pathway. An attacker who compromises a less-secured peripheral system (a third-party validation platform, a mobile payment app backend) and exploits an improperly secured API connection can potentially access the core parking management platform.
Real Threat Scenarios
Ransomware
Ransomware is the most operationally disruptive cybersecurity threat to parking operations. In a ransomware attack, malicious software encrypts the operator’s data and systems, rendering them inaccessible until a ransom is paid or systems are restored from clean backups.
For a parking operation, ransomware that affects the management system can mean: gates that don’t open (if gate control depends on the management server), no payment processing (if pay stations depend on cloud connectivity for transaction authorization), and loss of transaction history and permits.
The initial access vector is typically phishing (an employee clicks a malicious email link), credential compromise (stolen credentials used to access remote management tools), or exploitation of an unpatched vulnerability in internet-exposed systems.
Payment Card Data Compromise
Physical skimming at pay stations is the most direct payment card attack, but it’s not the only one. Pay station software that stores card data beyond PCI DSS requirements, management systems with inadequate access controls on stored transaction data, and integrations that pass raw card data through non-compliant systems all create payment data exposure risk.
PCI DSS compliance for parking operations is required if you accept card payments — which means essentially all operators. But compliance is a minimum baseline, not a guarantee of security. PCI-compliant systems can still have significant security weaknesses in areas that the standard doesn’t address.
Access Control Compromise
For parking facilities integrated with building access control (common in corporate campuses, hotels, and residential buildings), compromise of the parking system can extend to physical access control. A compromised credential database that includes access control credentials represents a physical security breach, not just a cybersecurity event.
Practical Risk Reduction Framework
Network Segmentation
The single highest-impact security architecture decision for parking systems is network segmentation: placing parking system devices on an isolated network segment that is not connected to the corporate network or to the internet except through controlled access points.
A properly segmented parking network means that a compromised pay station camera cannot directly access corporate financial systems; a compromised LPR camera cannot directly access the corporate email server. The attack surface is bounded.
Practical segmentation uses VLANs (Virtual Local Area Networks) to separate parking devices onto their own network segments, with firewall rules that allow only the specific connections required for parking system operation: pay stations to payment gateway, cameras to management server, management server to cloud platform.
This is not complex network engineering — a competent network administrator can implement basic segmentation in a day. But it requires that someone is responsible for the parking network architecture, and in many organizations, no one is.
Credential Management
Default credentials are the entry point for a significant fraction of IoT device compromises. The remediation is straightforward but requires operational discipline:
- Change default credentials on every device during installation (cameras, pay stations, network equipment, software platforms)
- Use unique, strong passwords for each device (password managers make this manageable)
- Enable multi-factor authentication (MFA) on all management platforms that support it
- Audit credentials periodically and rotate passwords when personnel changes occur
Privileged access management (PAM) tools that store and manage credentials securely, log access events, and rotate credentials automatically are appropriate for larger operations.
Patch Management
Unpatched software is the underlying vulnerability in a large percentage of security incidents. Parking system operators need a patch management process that covers:
- Pay station operating system and application software updates
- LPR camera and other camera firmware updates
- Network equipment firmware updates
- Parking management software updates (cloud-hosted platforms typically handle this automatically; on-premise deployments require deliberate scheduling)
“If it’s working, don’t touch it” is a common operational attitude toward software updates — and it’s a significant security risk. Establish a regular patching cadence (monthly for software, quarterly for firmware) and treat it as a maintenance requirement, not an optional activity.
Physical Security for System Access
Parking pay stations contain computers connected to payment and facility networks. Physical security controls for pay station cabinets should include:
- High-security key cylinders (not the generic cam locks found on low-security equipment enclosures)
- Tamper detection (door-open sensors that alert management systems)
- Regular inspection for skimmer devices or other unauthorized hardware additions
- Access logging for technician visits
For LPR and security cameras, tamper-resistant mounting and regular physical inspection for unauthorized device additions are appropriate.
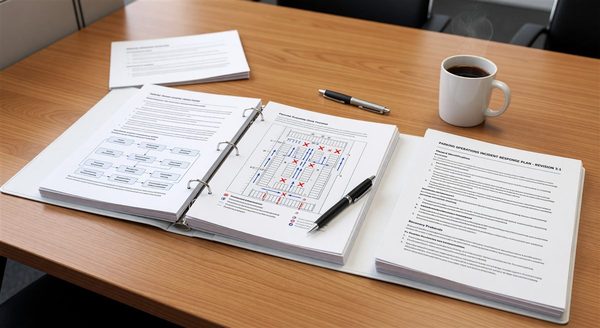
Incident Response Planning
When (not if) a security incident occurs, the difference between a manageable event and an operational disaster is largely determined by whether a response plan exists and whether it’s been tested.
A parking-specific incident response plan should address:
- Who is responsible for declaring an incident and initiating response
- How to isolate affected systems without taking the entire facility offline
- Backup procedures that allow transaction processing to continue in degraded mode while systems are restored
- Communication procedures for notifying customers if payment data is compromised (required by most state breach notification laws)
- Vendor contact procedures for PARCS vendor support during an incident
The parkingprofessional.com organization has developed industry guidance on cybersecurity requirements for parking operations that parallels the frameworks used in other critical infrastructure sectors — a useful starting point for operators developing formal security programs.
Working with Vendors on Security
Parking technology vendors have highly variable cybersecurity postures. Due diligence questions when evaluating vendors:
- Do you have a published cybersecurity policy or security program?
- What is your vulnerability disclosure process, and how quickly do you release patches?
- Does your software undergo third-party security testing (penetration testing, code audits)?
- What data do you collect, how long is it retained, and how is it protected?
- What is your incident response procedure if your platform is compromised?
Vendors who can answer these questions specifically have invested in security as a program. Vendors who deflect or provide vague answers haven’t — and that’s a material procurement risk.
Parking system cybersecurity isn’t a solved problem, and it won’t be. But operators who understand the attack surface, implement basic security hygiene, and maintain vendor accountability are dramatically better positioned than the operators who find out about their gaps in a ransomware negotiation.
The Parking BOXX team has covered cybersecurity for parking operators in depth — including PCI DSS compliance basics, NIST framework application, and penetration testing requirements for parking vendors — at their blog.